
A 256-bit key offers more possible combinations than any existing computer network can realistically search. But stolen credentials, compromised devices and future quantum attacks explain why strong mathematics alone cannot guarantee digital security.
November 6, 2026 — A video circulating on YouTube poses a striking question: Could a computer guess a 256-bit encryption key if it had been running continuously since the Big Bang?
For a uniformly random AES-256 key, even an extraordinarily powerful imaginary computer network would have an almost negligible chance of finding that exact key through exhaustive guessing. The central mathematical point is sound. The video also contains a major arithmetic error and treats several different cryptographic concepts as though they were interchangeable.
These distinctions matter for Americans protecting bank accounts, cryptocurrency wallets, medical records or private messages. They also matter for businesses and public agencies responding to the National Institute of Standards and Technology’s October 27, 2026, post-quantum transition guidance.
The Number Behind 256-Bit Encryption
A cryptographic key made of 256 independent random bits can take one of 2256 possible values, approximately 1.158 × 1077 combinations. The number has 78 decimal digits. Adding one truly random bit doubles the size of the keyspace.
The U.S. Advanced Encryption Standard (AES) supports 128-, 192- and 256-bit keys. The NIST FIPS 197 standard, originally published in 2001 and updated editorially in 2023, specifies the three AES variants. AES is symmetric encryption: authorized parties use the same secret key to encrypt and decrypt information.
With a properly generated random key, a secure implementation and no better attack, the attacker faces a keyspace far beyond any feasible classical brute-force search. That is a statement about current cryptographic knowledge, not a guarantee that no future mathematical or engineering weakness could ever be discovered.
How Many Universes Would It Take?
The source video breaks 2256 into eight factors of 232. Each factor is about 4.29 billion. It imagines processors, enormous facilities, billions of copies of those facilities, entire planets and galaxies devoted to trying candidate keys.
Start with 232 guesses per second, and multiply that processing capacity by four more factors of 232. The hypothetical system would produce 2160 guesses per second. Running it for 232 seconds, and repeating that duration 232 times, yields 2224 guesses.
That is still only 1/232 of the 256-bit keyspace. If those are distinct guesses against one uniformly random key, success would be approximately a one-in-4.29-billion chance. The scale is illustrative, not a description of an achievable machine. Exhausting the full keyspace would require a further factor of 232.
The Video’s Timeline Is Wrong
The narration claims that roughly four billion periods of about 127 years amount to 57 billion years. That multiplication is incorrect: using the rounded quantities gives roughly 507 billion years. Using the exact powers of two, 264 seconds is approximately 585 billion years.
So the video’s stated comparison with roughly 37 ages of the universe fits the rounded 507-billion-year figure, not 57 billion. Correcting the arithmetic does not change the larger finding: the imagined resources are astronomically impractical, and they still do not guarantee the target key would be found.
A Hash Is Not an Encryption Key
Cryptography encompasses different problems. AES encrypts and decrypts data with a secret key. A cryptographic hash function instead maps an input to a fixed-length output and is designed to resist certain ways of working backward or finding matching outputs.
NIST’s hash-function security-strength table lists 256-bit resistance for generic preimage attacks against SHA-256 but 128-bit resistance for generic collision attacks. The distinction reflects different attack goals, not a contradiction.
Cryptocurrency security is also more complicated than the bit length of a wallet’s secret. Private keys, digital signatures, hashing, wallet recovery phrases and custodial-account security are different parts of an overall system. A 256-bit number by itself does not ensure a system has 256 bits of security against every type of attack.
Why Criminals May Never Need to Break AES-256
Attackers routinely look for easier targets: phishing for login credentials, stealing wallet recovery phrases, infecting devices with malware, exploiting vulnerable applications or accessing services through improperly protected accounts.
An attacker who steals the valid decryption key, for example, can bypass the need to brute-force the encryption. Weak password choices and poor key generation can also undermine otherwise robust algorithms. An encrypted file is only as well protected as the key management and surrounding systems allow.
For individuals, that is why unique passwords, password managers, phishing-resistant multifactor authentication, device updates and carefully stored backup or recovery information remain essential.
The Quantum Computing Question
A future sufficiently capable fault-tolerant quantum computer could break certain commonly deployed public-key cryptographic systems. Algorithms including Shor’s threaten RSA and many elliptic-curve methods; this is a major reason organizations are planning migration to post-quantum cryptography.
For symmetric encryption such as AES, the best-known generic quantum speedup is different. Grover’s algorithm can reduce an idealized exhaustive search from a scale of roughly 2256 classical trials to around 2128 quantum search steps. But quantum steps are not simple equivalents of conventional processor guesses; quantum error correction, circuit resources and sequential operations impose formidable constraints. This does not mean practical AES-256 brute forcing has become possible.
NIST’s approach focuses particularly on replacing public-key mechanisms vulnerable to future quantum attacks while retaining strong symmetric cryptography where appropriate.
Why the U.S. Government Is Preparing Now
NIST finalized its first three post-quantum cryptography standards in August 2024. They include FIPS 203 for ML-KEM, a method of establishing shared secret keys that can then be used with symmetric encryption.
On October 27, 2026, NIST published the final NIST IR 8547, Transition to Post-Quantum Cryptography Standards. The report identifies algorithms that need to be replaced, along with migration considerations for federal agencies and technology suppliers.
One reason for urgency is the harvest now, decrypt later risk: adversaries can collect encrypted traffic today and hope to defeat some of its public-key protections with future quantum technology. This is not evidence that AES-256 has been cracked. Many real-world secure communications systems combine symmetric encryption with public-key methods used for key establishment or authentication.
For American government agencies, banks, healthcare providers and companies, future security planning means inventorying the cryptography they rely on, updating vulnerable protocols, and deciding which sensitive data must remain confidential for decades.
What Americans Should Take Away
There is no credible evidence that criminals are routinely breaking correctly implemented AES-256 by searching its entire random keyspace. But strong encryption does not by itself prevent stolen credentials, compromised devices, insecure services or future vulnerabilities in surrounding technologies.
The real lesson is not that security is guaranteed for the lifetime of the universe. It is that extremely strong mathematics protects against one kind of attack, while practical security depends on how the keys and systems are managed.
Watch: The Original Explanation and NIST’s Quantum Perspective
The original short is included to show the comparison examined in this fact-check. Its 57-billion-year calculation should not be treated as accurate.
Watch the original YouTube Short — this report corrects its arithmetic.
For an official explanation of the emerging quantum threat, watch NIST’s Post-Quantum Cryptography: The Good, the Bad, and the Powerful.
Sources and Further Reading
- NIST — FIPS 197, Advanced Encryption Standard (updated 2023)
- NIST — Hash Function Security Strengths
- NIST — IR 8547, Transition to Post-Quantum Cryptography Standards (October 2026)
- NIST — News Release Explaining the Post-Quantum Transition
- NIST — FIPS 203, ML-KEM Standard
- NIST — Original Featured Photo and Quantum Key Distribution Research (2007)
- NIST — Original David Wineland Photo and Editorial Permissions
- Original Video — Why 256-Bit Encryption Can’t Be Brute-Forced
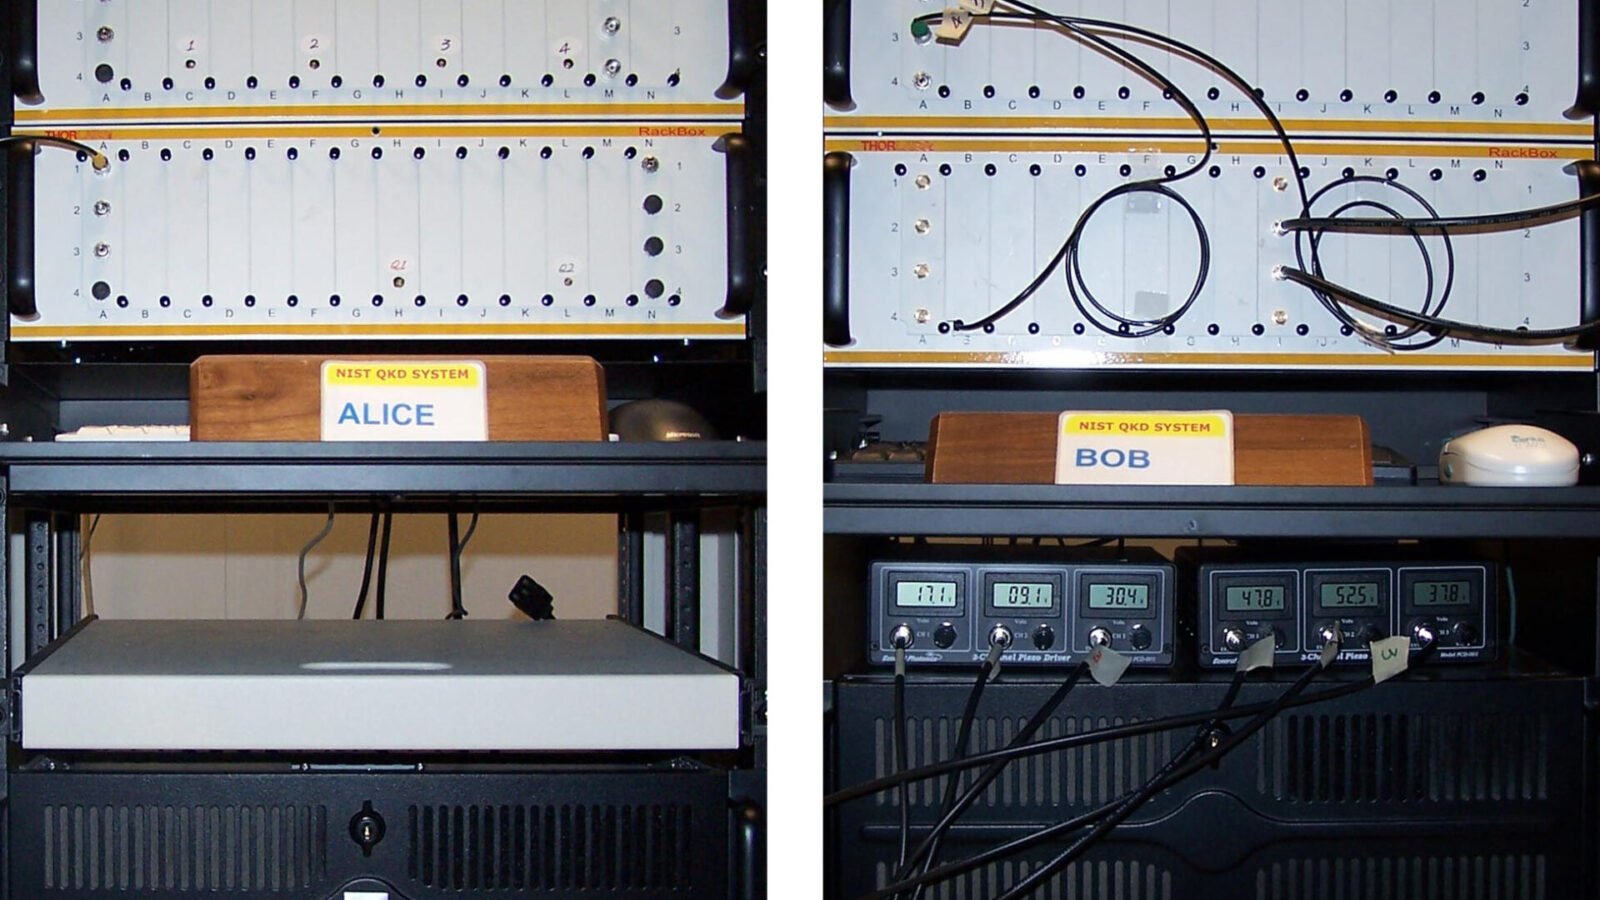
Editorial note: This report corrects the original video’s arithmetic and distinguishes AES encryption, hash resistance and cryptocurrency key security. The featured photograph depicts NIST quantum-key distribution apparatus from 2007—not a device used to brute-force AES-256. Featured image credit: NIST.